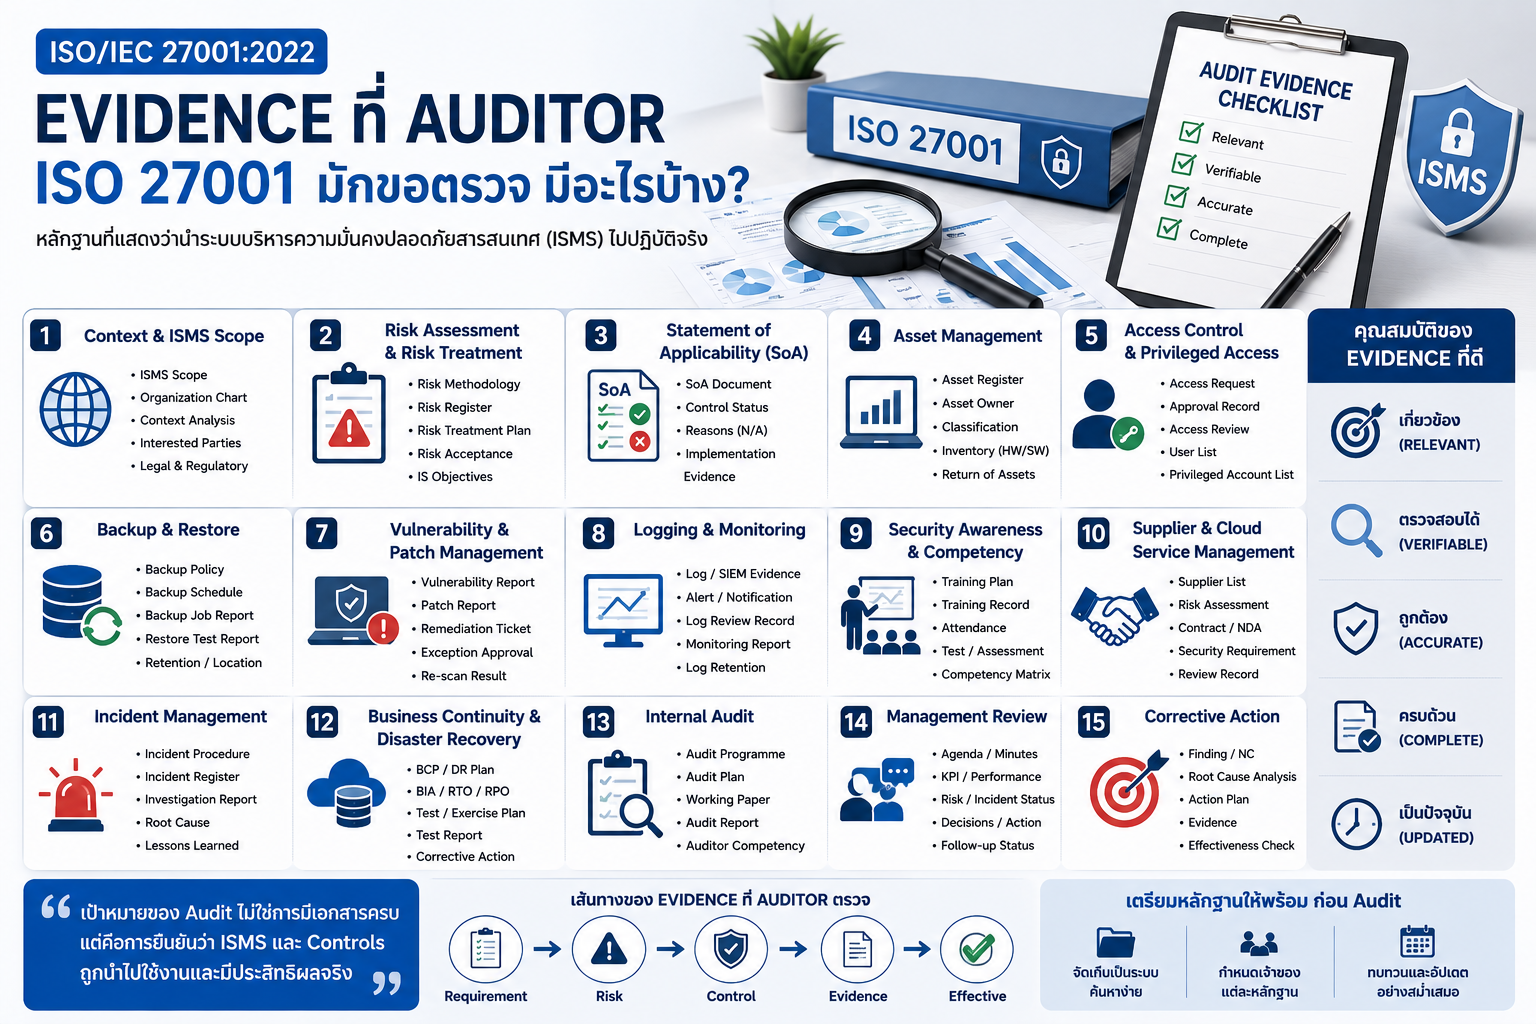

Evidence ในการตรวจ ISO 27001 คืออะไร
ในการตรวจ ISO/IEC 27001:2022 Auditor ไม่ได้พิจารณาเฉพาะว่าองค์กรมี Policy หรือ Procedure หรือไม่ แต่ต้องมีหลักฐานที่สามารถยืนยันได้ว่าสิ่งที่กำหนดไว้ถูกนำไปปฏิบัติจริง
ในหลักการ Audit นั้น Audit Evidence สามารถเป็น Record, ข้อเท็จจริง หรือข้อมูลอื่นที่เกี่ยวข้องกับ Audit Criteria และสามารถตรวจสอบยืนยันได้ ไม่จำเป็นต้องเป็นเอกสาร PDF เสมอไป
ดังนั้น Evidence ที่ Auditor ขออาจเป็นได้ทั้ง
- เอกสาร
- Record
- Screenshot
- System Configuration
- Log
- Ticket
- Email Approval
- Report
- การสัมภาษณ์
- การสังเกตการปฏิบัติงานจริง
ISO/IEC 27001 ใช้ Risk-based approach ในการบริหาร ISMS ดังนั้น Auditor มักมองความสัมพันธ์ระหว่าง Risk, Control และหลักฐานที่แสดงว่า Control ทำงานจริงด้วย
1. Evidence ด้าน Context และ ISMS Scope
Auditor อาจเริ่มจากการทำความเข้าใจว่า ISMS ขององค์กรครอบคลุมอะไร
Evidence ที่มักขอ เช่น
- ISMS Scope
- Organization Chart
- Process Map
- Context Analysis
- Interested Parties Register
- Legal and Regulatory Requirements
- รายการระบบและ Location ที่อยู่ใน Scope
สิ่งสำคัญคือข้อมูลในเอกสารต้องตรงกับการดำเนินงานจริง
ตัวอย่างเช่น ถ้า Scope ระบุว่าครอบคลุม Cloud Application แต่ Risk Register และ Asset Register ไม่มีระบบดังกล่าวเลย Auditor อาจตรวจต่อว่าการกำหนด Scope และ Risk Assessment สอดคล้องกันหรือไม่
2. Risk Assessment และ Risk Treatment
หัวข้อนี้เป็น Evidence สำคัญมาก เพราะ ISO 27001 ใช้แนวทางบริหารความเสี่ยงเป็นพื้นฐานของ ISMS
Auditor มักขอดู
- Risk Assessment Methodology
- Risk Criteria
- Risk Register
- Risk Owner
- Risk Treatment Plan
- Risk Acceptance
- Information Security Objectives
แล้วตรวจความสัมพันธ์ว่า
Risk → Treatment → Control → Evidence
เชื่อมโยงกันจริงหรือไม่
ตัวอย่าง Finding ที่พบได้คือ Risk Register มีรายการความเสี่ยง แต่ไม่มีการติดตาม Treatment หรือไม่มี Evidence ว่า Control ที่เลือกไว้ถูกนำไปใช้จริง
3. Statement of Applicability หรือ SoA
Statement of Applicability เป็นเอกสารสำคัญที่ Auditor มักขอในช่วงต้นของการ Audit
สิ่งที่ Auditor อาจตรวจ เช่น
- Control ใด Applicable
- Control ใด Not Applicable
- เหตุผลในการเลือกหรือไม่เลือก Control
- Implementation Status
- ความสัมพันธ์กับ Risk Treatment
- Evidence ของ Control ที่ระบุว่า Implemented
หาก SoA ระบุว่า Control ถูกนำไปใช้แล้ว Auditor อาจเลือก Sampling ไปตรวจระบบหรือ Record จริงเพื่อยืนยัน
4. Asset Management
Evidence ด้าน Asset Management อาจประกอบด้วย
- Asset Register
- Information Asset List
- Asset Owner
- Classification
- Device Inventory
- Software Inventory
- Cloud Service List
- การคืนทรัพย์สินเมื่อพนักงานลาออก
Auditor อาจสุ่มตรวจ Asset จริงเทียบกับ Register เพื่อดูว่าข้อมูล Update หรือไม่
ตัวอย่างเช่น Notebook ถูกส่งให้พนักงานใช้งาน แต่ไม่มี Serial Number หรือ Asset Owner ใน Asset Register
5. User Access และ Privileged Access
หัวข้อนี้มักถูกตรวจค่อนข้างละเอียด โดยเฉพาะองค์กรที่มีระบบสำคัญ
Evidence ที่ Auditor อาจขอ ได้แก่
- Employee List
- Active User List
- Resigned Employee List
- Access Request
- Approval Record
- Access Matrix
- Privileged Account List
- Access Review
- MFA Configuration
- Shared Account
- Service Account
จากนั้นอาจ Sampling เส้นทาง
Request → Approval → Provisioning → Review → Revocation
เพื่อดูว่าการบริหารสิทธิ์ทำงานตลอดทั้งวงจรหรือไม่
6. Backup และ Restore
แค่มี Backup Report อาจยังไม่เพียงพอ
Auditor อาจขอ Evidence เช่น
- Backup Policy
- Backup Schedule
- Backup Configuration
- Backup Job Status
- Failed Backup Report
- Retention Setting
- Backup Location
- Access Control
- Restore Test Report
ประเด็นสำคัญคือองค์กรต้องสามารถแสดงได้ว่า กู้คืนข้อมูลได้จริง
ดังนั้น Restore Test มักมีน้ำหนักมากกว่า Screenshot ที่แสดงว่า Backup Job ขึ้น Success เพียงอย่างเดียว
7. Vulnerability และ Patch Management
สำหรับ Technological Controls Auditor อาจขอ Evidence เช่น
- Vulnerability Scan Report
- Patch Report
- Critical Vulnerability List
- Remediation Ticket
- Exception Approval
- SLA
- Evidence หลังแก้ไข
- Re-scan Result
Auditor มักตรวจว่า Vulnerability ที่พบถูกนำไปติดตามและแก้ไขจนจบหรือไม่ ไม่ใช่เพียงมี Scan Report
8. Logging และ Monitoring
Evidence อาจประกอบด้วย
- Security Log
- System Log
- Firewall Log
- Authentication Log
- SIEM Dashboard
- Alert
- Incident Ticket
- Monitoring Report
- Log Retention Setting
Auditor อาจถามต่อว่า
- ใคร Review Log
- Review บ่อยแค่ไหน
- เมื่อพบ Alert มีการดำเนินการอย่างไร
- Log เก็บไว้นานเท่าไร
- มีการป้องกันการแก้ไข Log หรือไม่
ดังนั้น Screenshot หน้า Dashboard เพียงอย่างเดียวอาจยังไม่เพียงพอหากไม่มีหลักฐานการติดตาม
9. Security Awareness และ Competency
Auditor มักตรวจว่าบุคลากรมีความรู้เหมาะสมกับหน้าที่ และได้รับ Awareness ตามที่องค์กรกำหนดหรือไม่
Evidence ที่ควรเตรียม เช่น
- Training Plan
- Training Record
- Attendance
- Test Result
- Awareness Material
- Employee List
- Competency Matrix
- Certificate
- Training สำหรับพนักงานใหม่
Auditor อาจเปรียบเทียบ Employee List กับ Training Record เพื่อดูว่ามีพนักงานตกหล่นหรือไม่
10. Supplier และ Cloud Service
หากองค์กรใช้ Supplier หรือ Cloud Service ที่เกี่ยวข้องกับข้อมูลหรือระบบสำคัญ Auditor อาจขอดู
- Supplier List
- Supplier Risk Assessment
- Due Diligence
- Contract
- NDA
- Security Requirements
- SLA
- Supplier Review
- Cloud Service Assessment
- Incident Notification Requirement
Evidence ควรแสดงให้เห็นว่าองค์กรไม่ได้ประเมิน Supplier เฉพาะก่อนเริ่มใช้งาน แต่มีการติดตามหลังจากนั้นด้วย
11. Incident Management
Auditor อาจขอ
- Incident Management Procedure
- Incident Register
- Security Event
- Ticket
- Investigation Report
- Root Cause
- Corrective Action
- Lessons Learned
ในบางกรณี Auditor จะเลือก Incident จริงหนึ่งเหตุการณ์แล้ว Trace ตั้งแต่
Detection → Classification → Escalation → Response → Closure → Lessons Learned
เพื่อดูว่า Procedure ถูกนำไปใช้งานจริงหรือไม่
12. Business Continuity และ Disaster Recovery
Evidence ที่มักพบในการ Audit ได้แก่
- BCP
- DR Plan
- Business Impact Analysis
- Recovery Requirement
- RTO / RPO
- DR Test
- Exercise Report
- Test Finding
- Corrective Action
จุดสำคัญไม่ใช่แค่มี BCP หรือ DR Plan แต่ต้องสามารถแสดงได้ว่าเคยทดสอบ และผลจากการทดสอบถูกนำไปปรับปรุงหรือไม่
13. Internal Audit
แน่นอนว่า Auditor ภายนอกหรือ Certification Auditor มักตรวจ Internal Audit ที่องค์กรดำเนินการก่อนหน้า
Evidence อาจประกอบด้วย
- Audit Programme
- Audit Plan
- Audit Checklist
- Audit Working Paper
- Sampling
- Audit Findings
- Internal Audit Report
- Auditor Competency
- Corrective Action Tracking
ISO 19011 ให้แนวทางเกี่ยวกับหลักการ Audit การบริหาร Audit Programme การดำเนินการ Audit และ Competence ของ Auditor
หาก Internal Audit มีแต่ Checklist ที่ตอบ Yes ทุกข้อ แต่ไม่มี Sampling หรือ Evidence Auditor อาจตั้งคำถามเรื่องประสิทธิผลของ Internal Audit ได้
14. Management Review
Evidence ที่มักขอ เช่น
- Management Review Agenda
- Meeting Minutes
- Attendance
- KPI
- Risk Status
- Incident Status
- Audit Result
- Corrective Action
- Decision และ Action Item
Auditor ไม่ได้ดูเพียงว่ามีประชุมหรือไม่ แต่จะดูว่าผู้บริหารได้ Review ประเด็นสำคัญของ ISMS และมีการตัดสินใจหรือ Action จากการประชุมหรือไม่
15. Corrective Action
เมื่อมี Finding หรือ Nonconformity Auditor อาจขอตรวจ
- Finding
- Correction
- Root Cause Analysis
- Corrective Action Plan
- Action Owner
- Due Date
- Evidence หลังแก้ไข
- Effectiveness Verification
สิ่งที่ควรระวังคือการปิด Finding เพียงเพราะ “ดำเนินการแล้ว”
ควรมี Evidence ที่แสดงว่าการแก้ไขสามารถลดโอกาสเกิดปัญหาเดิมซ้ำได้จริง
Evidence ไม่จำเป็นต้องเป็นเอกสารทุกอย่าง
ข้อเข้าใจผิดที่พบได้บ่อยคือองค์กรพยายามสร้างเอกสารเพิ่มจำนวนมากก่อน Audit
แต่ในทางปฏิบัติ Evidence อาจเป็นข้อมูลจากระบบจริงได้
ตัวอย่างเช่น
| สิ่งที่ Auditor ต้องการยืนยัน | Evidence ที่อาจใช้ |
| User ถูกปิดหลังลาออก | Active Directory / M365 |
| Backup ทำงาน | Backup Job / Log |
| Restore ได้จริง | Restore Test |
| มี Access Review | Review Record |
| Vulnerability ถูกแก้ | Re-scan / Ticket |
| Training ครบ | Employee List + Training Record |
| Incident ถูกจัดการ | Incident Ticket |
| Supplier ถูกประเมิน | Supplier Assessment |
หลักสำคัญคือ Evidence ต้อง เกี่ยวข้องกับสิ่งที่ตรวจและสามารถ Verify ได้
เตรียม Evidence ก่อน Audit อย่างไรให้ไม่วุ่น
ก่อนวัน Audit แนะนำให้ทำ Evidence List แยกตาม Clause หรือ Control แล้วกำหนด Owner ชัดเจน
ตัวอย่าง
Access Control
- Owner: IT
- Evidence: User List, Approval, Access Review
Training
- Owner: HR
- Evidence: Employee List, Training Record
Supplier
- Owner: Procurement
- Evidence: Supplier Assessment, Contract
วิธีนี้ช่วยลดปัญหา Auditor ถามแล้วทุกคนต้องวิ่งหาไฟล์ระหว่าง Audit
แต่ไม่ควรสร้าง Evidence ใหม่ย้อนหลังเพียงเพื่อให้ดูครบ ควรใช้ข้อมูลจากการปฏิบัติงานจริงเป็นหลัก
สรุป
Evidence ที่ Auditor ISO 27001 มักขอตรวจไม่ได้มีเพียง Policy และ Procedure แต่ครอบคลุมตั้งแต่
Risk, SoA, Asset, Access Control, Backup, Vulnerability, Log, Training, Supplier, Incident, DR, Internal Audit, Management Review และ Corrective Action
สิ่งสำคัญคือองค์กรต้องสามารถเชื่อมโยงให้เห็นว่า
Requirement → Risk → Control → Evidence
ทำงานสัมพันธ์กันจริง
เพราะเป้าหมายของ Audit ไม่ใช่การพิสูจน์ว่าองค์กร “มีเอกสารครบ” แต่คือการยืนยันว่า ISMS และ Security Controls ถูกนำไปใช้งานและมีประสิทธิผลจริง
ต้องการตรวจ Evidence ก่อน Certification Audit?
DataFlow Consult ให้บริการ Internal Audit ISO/IEC 27001:2022 และ IT Audit ครอบคลุม Clause 4–10, Statement of Applicability, Annex A และ Technical Evidence พร้อม Sampling และสรุป Findings ก่อน Certification หรือ Surveillance Audit
Email: contact@dataflowconsult.com
โทร: 063-4563698